How to Fix DNS Leakage While Connected to VPN on Windows 11
 Written by Elena Rostova (Senior Cybersecurity Researcher)
•
Reviewed by Marcus Vance, CCNP
•
Updated October 2026
Understanding DNS Leaks in Windows 11
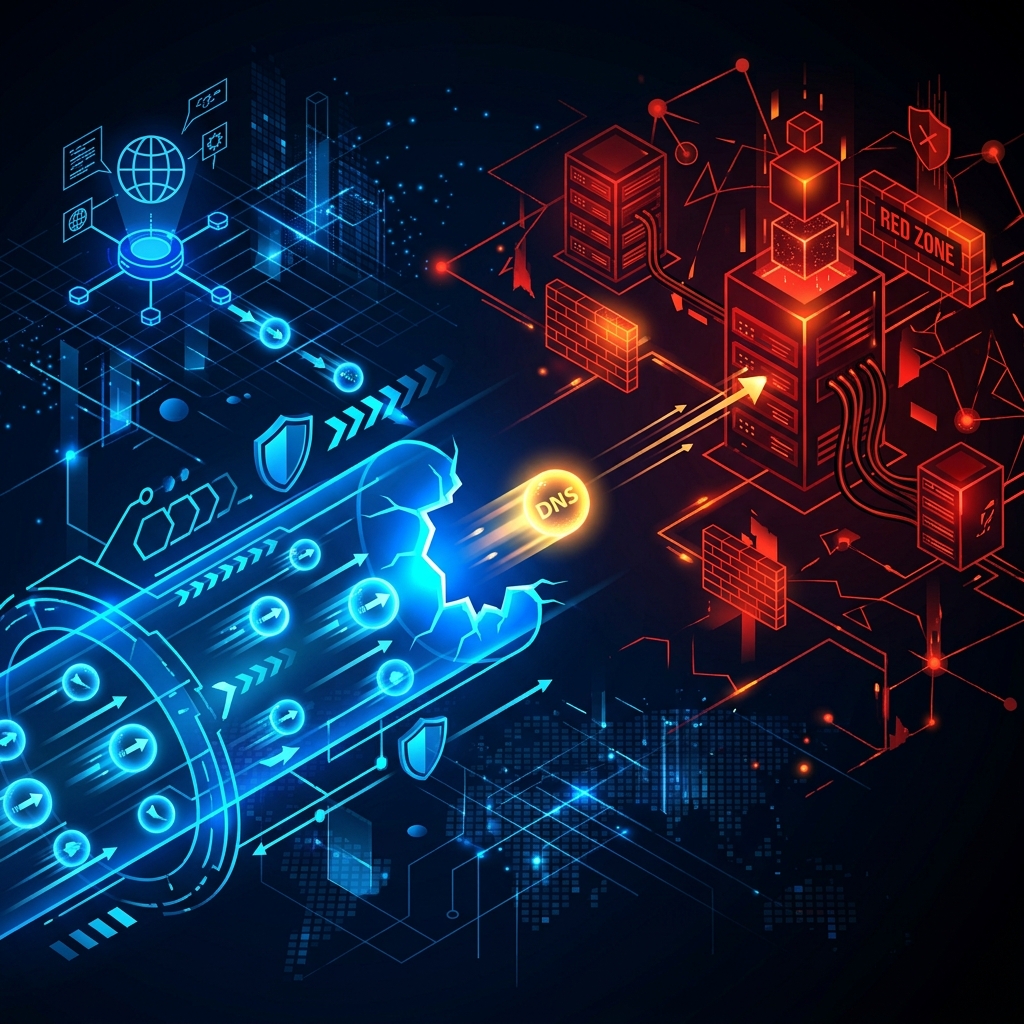
A Virtual Private Network (VPN) is designed to encrypt your internet traffic and route it through a secure tunnel, masking your IP address and protecting your browsing privacy. However, a critical security flaw known as a DNS leak can completely undermine this protection.
When you visit a website, your system relies on the Domain Name System (DNS) to translate human-readable domain names (like example.com) into numerical IP addresses. Under normal VPN operation, these DNS queries should be handled exclusively by the secure DNS servers provided by your VPN vendor. A DNS leak occurs when Windows 11 bypasses the encrypted VPN tunnel and routes these name resolution requests to your Internet Service Provider (ISP) or local network DNS server instead.
Why Windows 11 is Particularly Vulnerable to DNS Leaks
Windows 11 includes aggressive networking features designed to maximize connection speed. While beneficial for unencrypted web browsing, these features often interfere with VPN routing tables:
- Smart Multi-Homed Name Resolution (SMHNR): This feature sends DNS requests across all available network adapters (Wi-Fi, Ethernet, and VPN) simultaneously, adopting whichever server responds fastest. Often, your local ISP's DNS responds faster than the VPN server, triggering a leak.
- IPv6 Fallback: If your VPN provider only tunnels IPv4 traffic, Windows 11 may transmit IPv6 DNS queries outside the encrypted tunnel.
- Teredo and Tunneling Protocols: Built-in transition technologies in Windows can create secondary pathways that bypass active VPN adapters.
How to Verify if You Have a DNS Leak
Before applying fixes, confirm whether your system is leaking DNS requests:
- Connect to your VPN server.
- Visit a reputable DNS leak testing platform like
dnsleaktest.comorbrowserleaks.com/dns. - Run an extended test.
- Review the results: If you see your actual ISP's name or location listed alongside or instead of your VPN provider's DNS servers, your system has an active DNS leak.
Step-by-Step Fixes for Windows 11 DNS Leaks
1. Disable Smart Multi-Homed Name Resolution
Disabling SMHNR prevents Windows 11 from querying local network interfaces when connected to a VPN. You can disable this via the Group Policy Editor (Windows 11 Pro/Enterprise) or the Windows Registry (Windows 11 Home).
Via Local Group Policy Editor (Windows 11 Pro & Enterprise):
- Press Win + R, type
gpedit.msc, and press Enter. - Navigate to: Computer Configuration > Administrative Templates > Network > DNS Client.
- Locate and double-click Turn off smart multi-homed name resolution.
- Select Enabled, then click Apply and OK.
Via Windows Registry (Windows 11 Home):
- Press Win + R, type
regedit, and press Enter. - Navigate to:
HKEY_LOCAL_MACHINE\Software\Policies\Microsoft\Windows NT\DNSClient - If
DNSClientdoes not exist, right-clickWindows NT, select New > Key, and name itDNSClient. - Right-click in the right pane of
DNSClient, select New > DWORD (32-bit) Value, and name itDisableSmartNameResolution. - Double-click
DisableSmartNameResolutionand set its value to1.
2. Disable IPv6 Support on Your Active Adapter
If your VPN provider does not support native IPv6, disabling it at the adapter level stops Windows 11 from making out-of-band IPv6 DNS requests.
- Press Win + R, type
ncpa.cpl, and press Enter to open Network Connections. - Right-click your active network adapter (Wi-Fi or Ethernet) and select Properties.
- In the Networking tab, scroll down and uncheck Internet Protocol Version 6 (TCP/IPv6).
- Click OK to save the settings.
3. Clear and Reset the Windows DNS Cache
Cached DNS entries stored before connecting to the VPN can leak requests even after fixing settings. To flush stale records:
- Press Win + S, type
cmd, right-click Command Prompt, and select Run as administrator. - Type the following commands sequentially, pressing Enter after each:
ipconfig /flushdnsipconfig /registerdnsnetsh winsock reset
Restart your computer to complete the network stack reinitialization.
4. Configure Strict DNS Settings in Windows 11
You can manually enforce custom DNS servers or secure DNS protocols directly within Windows 11 settings to prevent default ISP fallbacks. For detailed information on DNS client behavior, refer to the Microsoft Learn DNS Client Resolution documentation.
- Open Settings (Win + I) and go to Network & internet.
- Select your connected network (Wi-Fi or Ethernet).
- Next to DNS server assignment, click Edit.
- Change the setting to Manual, enable IPv4, and input secure public DNS addresses (such as Cloudflare's
1.1.1.1or Quad9's9.9.9.9) if your VPN client doesn't automatically override network properties. Learn more about secure DNS standards from Cloudflare's DNS Learning Center.
5. Enable Native Leak Protection in Your VPN Client
Most enterprise-grade and commercial VPN clients include built-in mechanisms to prevent leaks. Ensure the following options are enabled inside your VPN app settings:
- IPv6 Leak Protection: Blocks or tunnels IPv6 traffic automatically.
- DNS Leak Protection: Forces all DNS queries through the VPN's internal tap adapter.
- Kill Switch: Automatically blocks all outbound internet traffic if the VPN connection drops unexpectedly.
Conclusion
DNS leaks represent a significant threat to online anonymity on Windows 11 due to OS-level networking optimizations like Smart Multi-Homed Name Resolution and aggressive interface prioritization. By disabling SMHNR, flushing your local DNS cache, managing IPv6 configurations, and leveraging your VPN's native kill switch features, you ensure that your DNS traffic remains fully encrypted within your secure tunnel.
Related Articles
Elena holds an M.S. in Information Security with 9+ years auditing VPN tunnels, WebRTC packet leaks, and defensive cyber architectures.
View all guides by Elena