How to Route Specific Application Traffic Through a VPN on Windows 11
Understanding Split Tunneling on Windows 11
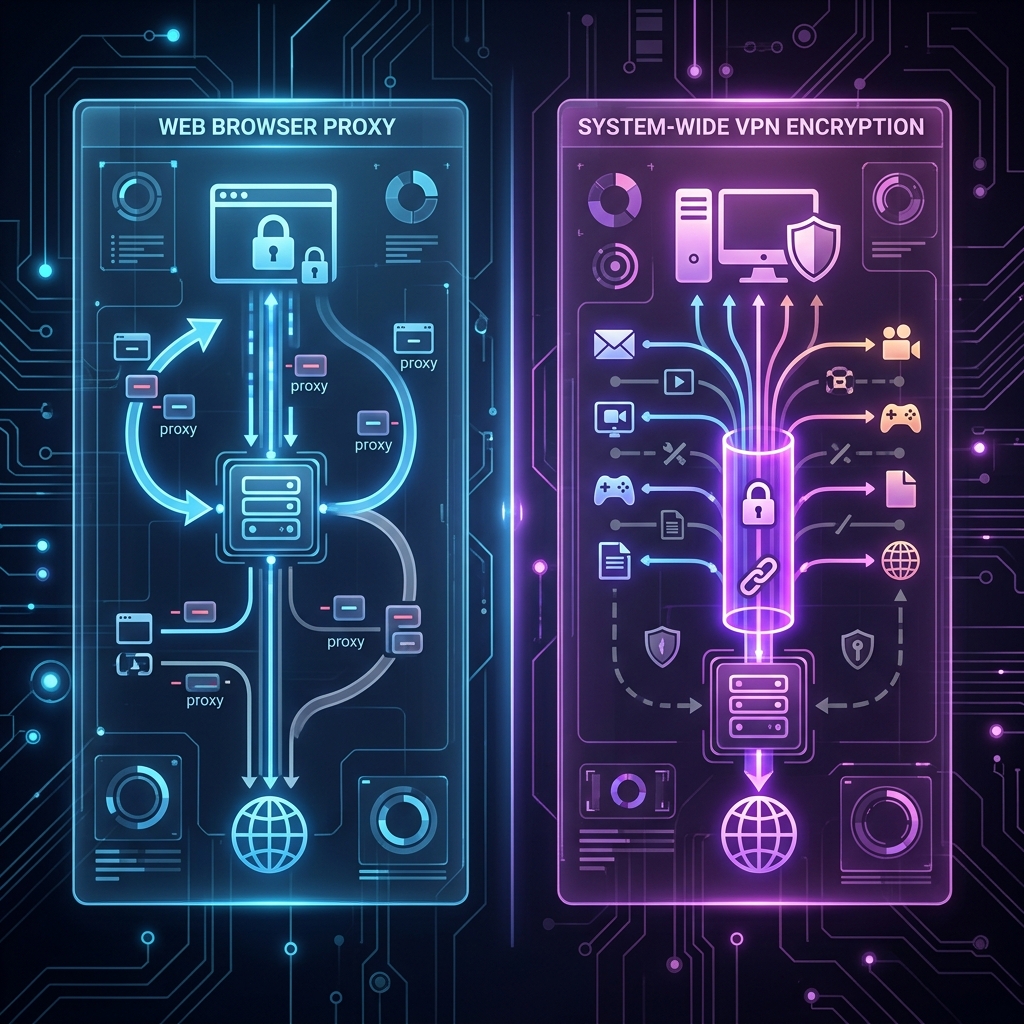
By default, when you activate a Virtual Private Network (VPN) connection on Windows 11, the OS modifies your default gateway. This routes 100% of your inbound and outbound internet traffic through an encrypted tunnel to the remote VPN server. While this offers maximum privacy, it is not always ideal.
Routing all traffic through a VPN can cause unnecessary latency in online games, prevent access to local network devices like smart printers or Network Attached Storage (NAS) devices, and trigger fraud alerts on online banking portals. The solution is app-based split tunneling—a network routing feature that sends specific application traffic through the encrypted VPN interface while allowing all other software to connect directly to your local Internet Service Provider (ISP).
Method 1: Using Built-in VPN Client Split Tunneling (Recommended)
The most stable and straightforward way to route specific apps through a VPN in Windows 11 is using the app-based split tunneling feature built into most modern commercial VPN clients (such as ExpressVPN, NordVPN, Surfshark, or Mullvad).
Step-by-Step Configuration:
- Disconnect from your VPN server inside your provider's desktop application.
- Open the app's Settings or Preferences menu (usually represented by a gear icon).
- Navigate to the Split Tunneling or Network Rules section.
- Enable Split Tunneling and select the policy option: 'Only allow selected apps to use the VPN' (or 'App-based split tunneling').
- Click Add Application or Browse, then navigate to the executable file (
.exe) of the target software (e.g.,C:\Program Files\Google\Chrome\Application\chrome.exe). - Save your settings and reconnect to the VPN server.
Once connected, Windows 11 will isolate the networking sockets for the chosen executables, routing their packets through the virtual network adapter (TAP/TUN interface) created by your VPN software.
Method 2: Using WireGuard AllowedIPs or Custom Route Tables
If you connect to a self-hosted VPN (like WireGuard or OpenVPN) or use native Windows 11 VPN configurations without a proprietary client, app routing requires manual IP routing or protocol configuration.
While Windows 11 route tables operate on destination IP addresses rather than executable process IDs, you can achieve destination-based split tunneling via the official WireGuard client by editing your configuration file.
Configuring Split Tunneling in WireGuard:
By editing the AllowedIPs directive in your WireGuard configuration file (.conf), you control which destination subnet ranges enter the VPN interface:
- Full Tunnel Default:
AllowedIPs = 0.0.0.0/0, ::/0 - Split Tunnel Example:
AllowedIPs = 104.16.0.0/12, 172.64.0.0/13(Routes traffic destined only for specific IP subnets through the tunnel).
Method 3: Advanced Process Isolation via ForceBindIP
For power users who need granular process-level binding on standard Windows interfaces without relying on client software, utility tools like ForceBindIP allow you to bind a specific application process directly to the local IP address assigned to your VPN network interface card (NIC).
How to Bind an App to the VPN Interface:
- Open the Windows Terminal or PowerShell as Administrator.
- Find the IP address of your active VPN adapter by running:
ipconfig /all - Note the IPv4 address assigned to the VPN Virtual Adapter (e.g.,
10.8.0.2). - Run your target application using ForceBindIP, passing the VPN IP address and the app path:
ForceBindIP64.exe 10.8.0.2 "C:\Program Files\Mozilla Firefox\firefox.exe"
This forces the Windows Winsock layer to bind all socket requests generated by that specific process ID to the designated VPN network interface.
Verifying App Tunneling and Preventing DNS Leaks
Configuring split tunneling creates potential privacy edge cases, such as DNS leaks, where your app's web requests travel through the encrypted VPN, but its domain name lookups (DNS queries) bypass the VPN and expose your browsing history to your ISP. To understand how Windows handles network traffic prioritizing and interface routing, consult the official Microsoft Networking Documentation.
How to Test Your Configuration:
- IP Check: Open the app routed through the VPN (e.g., a specific browser) and visit a site like
dnsleaktest.comoricanhazip.com. Verify that the IP address matches your VPN server location. - Direct Check: Open an unrouted browser (e.g., Microsoft Edge) and visit the same site. Verify that it displays your real ISP IP address.
- DNS Leak Test: Run an Extended DNS Leak Test inside the VPN-routed app to ensure that DNS queries are going exclusively to the VPN's secure DNS resolvers rather than your local router's DNS.
Summary Checklist for Windows 11 VPN Routing
Routing application traffic selectively optimizes both speed and operational security. Always ensure your VPN client is updated to the latest build, as updates to the Windows 11 Filtering Platform (WFP) drivers frequently patch socket leakage bugs associated with process-based routing.
Related Articles